DOJ Disrupts North Korean Remote IT Worker Schemes: 14 Indicted, Two Americans Arrested, About 187 Devices Seized in Texas
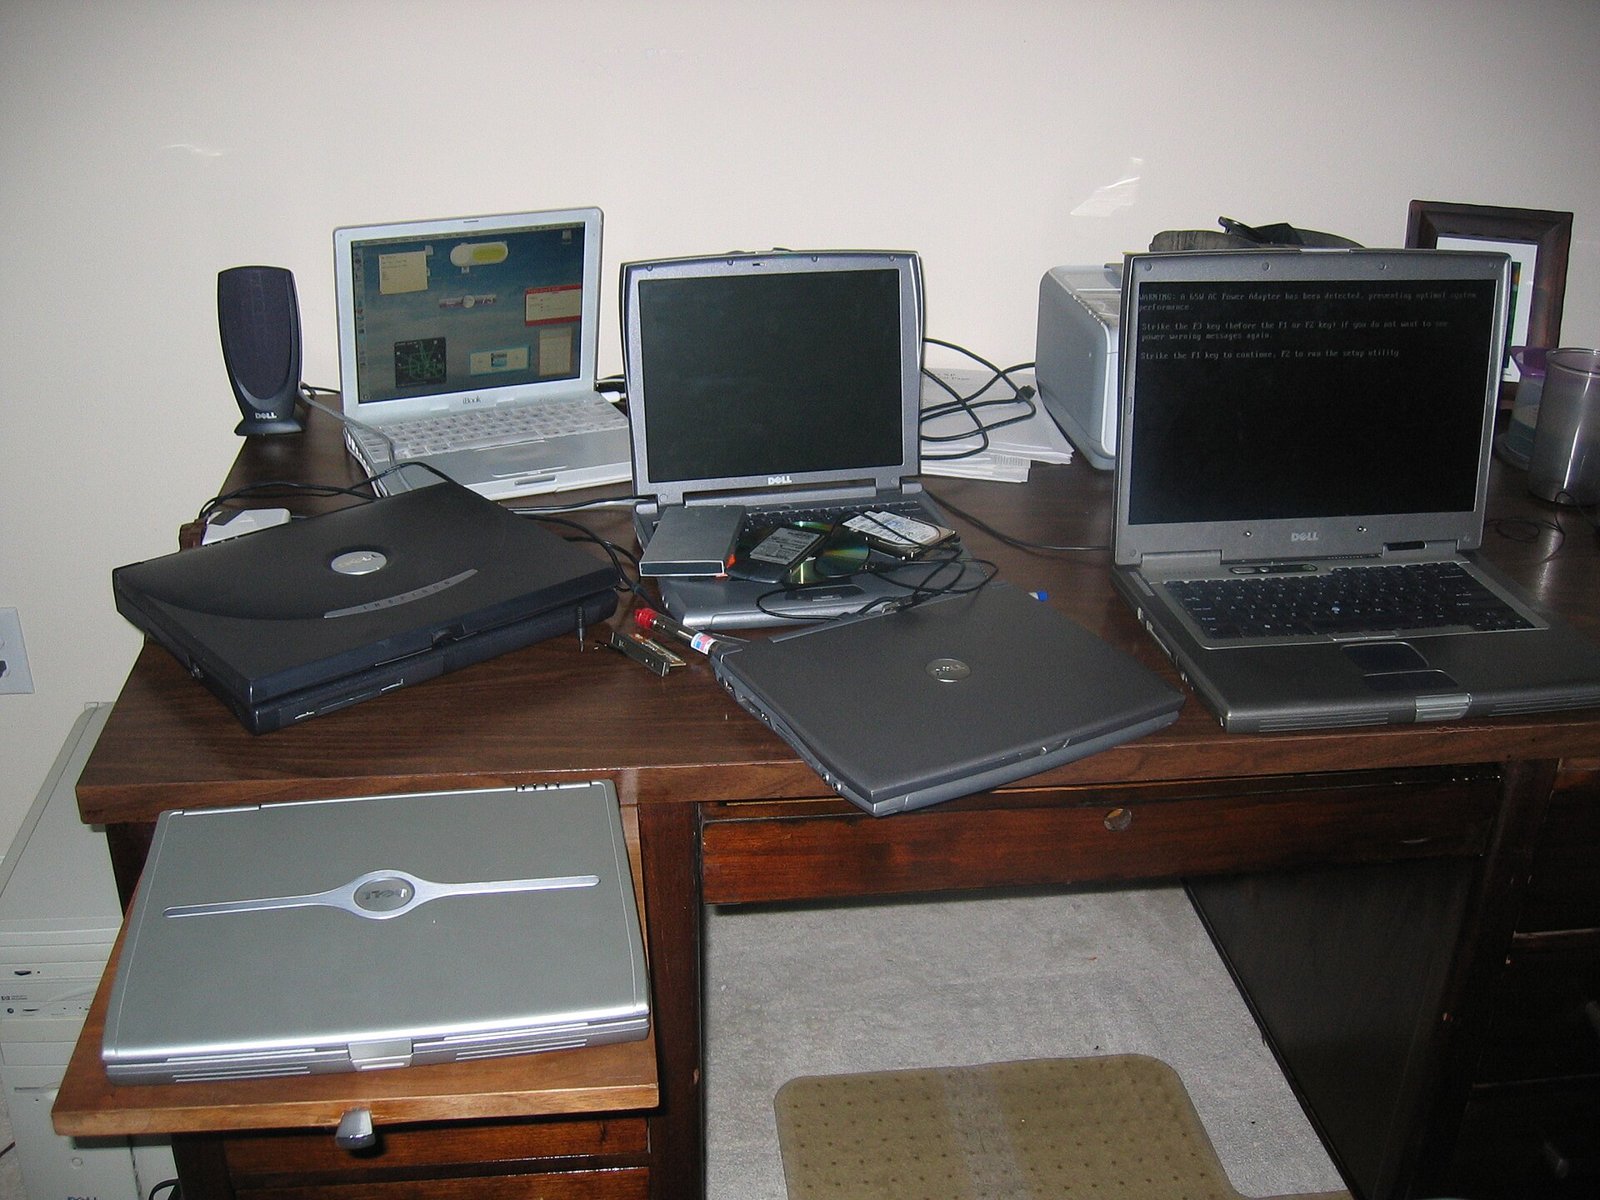
The Justice Department on October 13 announced coordinated actions against North Korea's remote IT worker schemes: the U.S. Attorney's Office for the Northern District of Ohio unsealed a four-count indictment charging 14 defendants; two U.S. citizens were arrested; and the FBI searched more than 40 Texas residences believed to operate as “laptop farms,” seizing approximately 187 laptops and KVM (keyboard, video, mouse) devices used by DPRK IT workers.
The two arrested are Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas. The indictment also charges 10 Chinese nationals based in China — Sun Sheng Ming, Pei Li Guang, Weng Shou Cheng, Han Guo Bin, Wang Jian Jun, Sheng Zhang Kun, Zhang Wei Ping, Zhang Li Ping, Yu Yang and Jin Long — while the identities of two additional defendants remain under seal. The charges include wire fraud conspiracy, money laundering conspiracy, conspiracy to commit identity theft and aggravated identity theft.
According to the department, from 2019 to in or around July 2025, North Korean IT workers used stolen or fabricated identity documents, VPNs and proxy infrastructure to appear to be U.S.-based workers and obtain remote positions at U.S. companies, while U.S.-based facilitators received and hosted victim companies' laptops at their homes — the “laptop farms” — installed remote-access software and transferred earnings to DPRK-controlled accounts in exchange for a share of the proceeds. The scheme impacted more than 70 U.S. company employers in sectors including health care, communications, cyber support, retail and manufacturing, across Ohio, 16 additional states and the District of Columbia, and generated approximately $3 million in revenue that prosecutors say is believed to have been sent to sanctioned DPRK-controlled entities.
In “Operation Lonestar Roundup,” the FBI conducted the Texas searches between September 21 and 25. The FBI said U.S. cybersecurity firm CrowdStrike has identified this group of DPRK IT workers and their helpers as “Famous Chollima,” and the FBI on the same day published a public service announcement with guidance for U.S. companies on detecting the threat.
“North Korea's rogue regime uses its pervasive IT worker schemes to raise revenue for various illicit purposes, including the development of weapons that could ultimately target the United States or its allies,” said Assistant Attorney General for National Security John A. Eisenberg. He said the National Security Division and its law enforcement partners will use every available tool to track down anyone assisting the DPRK.
The department noted that the details in the court documents are merely allegations, and all defendants are presumed innocent until proven guilty beyond a reasonable doubt in a court of law.
(Source: U.S. Department of Justice)
Source: U.S. Department of Justice
Published by GSM · USA (original Chinese edition)
Photo: 图:桌上多台笔记本电脑(示意)。摄影:.imelda,CC BY-SA 2.5,来源:Wikimedia Commons