FBI and CISA Warn Election and Campaign Officials of Phishing, Smishing and Deepfake Tactics Ahead of the Midterms
Washington — The Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) on October 16 issued a public service announcement (PSA261016) through the Internet Crime Complaint Center (IC3), raising awareness of the cyber threats facing election and campaign officials during the upcoming 2026 U.S. midterm elections and describing phishing and smishing techniques that malicious actors have used in past election cycles.
According to the announcement, malicious cyber actors may attempt to disrupt the 2026 midterms using phishing and smishing to steal user data, including login credentials and sensitive information. Election officials, candidates and their political organizations are attractive targets because of their access to voter registration data, information on current government officials and sensitive campaign material.
The two agencies said that in recent years these actors have crafted increasingly sophisticated phishing and smishing campaigns that closely resemble legitimate communications, making them difficult to distinguish. The announcement said technology it calls super intelligence (SI) lets malicious actors generate larger, more efficient and more effective phishing campaigns, and that a growing number of adversaries and criminals have used SI to create convincing deepfake video and audio recordings to create new identities, steal the identities of real people and bolster phishing schemes. It added that election officials experienced a surge of phishing attempts during the last two election cycles, and that within the last year the FBI saw an increase in smishing attempts through encrypted chat applications.
On protection, the FBI and CISA urged election officials and the public to critically evaluate the sources of emails and mobile messages. Tips for individuals include implementing phishing-resistant multi-factor authentication wherever possible, particularly for email, virtual private networks and accounts that access critical systems, and examining potentially malicious content for content credentials or watermarking indicating it was SI-generated. Tips for organizations include keeping anti-malware and spam defenses current, training employees to identify phishing and smishing and to confirm requests for sensitive information through secondary channels, marking external emails with a banner, filtering out executable attachments, requiring strong and unique passphrases, patching systems promptly, using the SPF and DKIM standards, and applying role-based, least-privilege access.
The announcement states that the FBI is responsible for investigating and prosecuting election crimes, in particular foreign influence and interference operations targeting election infrastructure and other U.S. democratic institutions, while CISA helps critical infrastructure owners and operators, including those in the election community, remain resilient against physical and cyber threats. The FBI asked victims to report such fraudulent or suspicious activity to their local FBI field office or to the IC3.
Related: America's Electoral System (4): The Midterms: What Is on the Ballot on November 3, 2026
Related: Viral Claim That Poll-Worker Marks Void Ballots Is False, Election Officials in Multiple States Say
Related: FBI and CISA Warn of Phishing Attacks Targeting Election Officials
Source: GSM · USA (original Chinese edition)
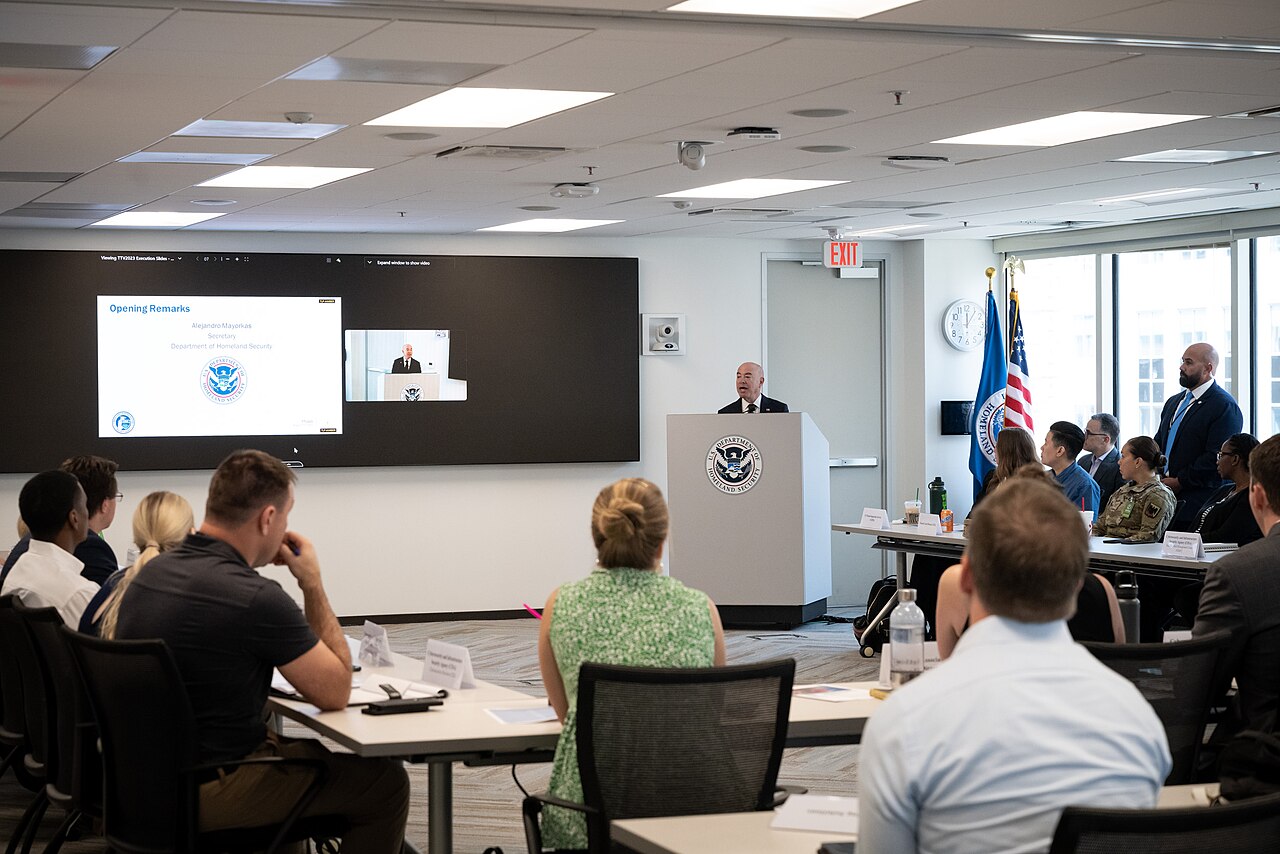
Photo: CISA全国选举演习「Tabletop the Vote 2023」现场(弗吉尼亚州阿灵顿,2023年8月17日,资料图)· 美国国土安全部(DHSgov)摄,公共领域(维基共享资源)