Berlin Privacy Watchdog Finds Four German Parties Breached the GDPR by Targeting Facebook Users on Political Interests; Reprimands Issued, No Fines
Berlin, Germany — The Berlin Commissioner for Data Protection and Freedom of Information (BlnBDI) has found that four German political parties breached the General Data Protection Regulation (GDPR) by targeting Facebook users based on their political interests during the 2021 federal election. The privacy group noyb published the closing notices, dated September 24, 2026, on October 21.
The decisions cover the CDU, the SPD, the Greens and The Left; a case involving the AfD is still pending. According to noyb, the authority found no legal basis, such as consent, for the targeting, and issued reprimands, but no fines or ban. The underlying data was originally collected by ZDF Magazin Royale and the Who Targets Me project, and noyb filed its complaints in March 2023.
Political opinions are special-category data under Article 9 of the GDPR, and selecting voters by interests that reveal political views requires a legal basis. The outcome confirms that advertisers bear responsibility for interest-based targeting of sensitive data, after a process that spanned a further federal election and the arrival of the EU's Transparency and Targeting of Political Advertising regulation (TTPA).
Source: GSM · USA (original Chinese edition)
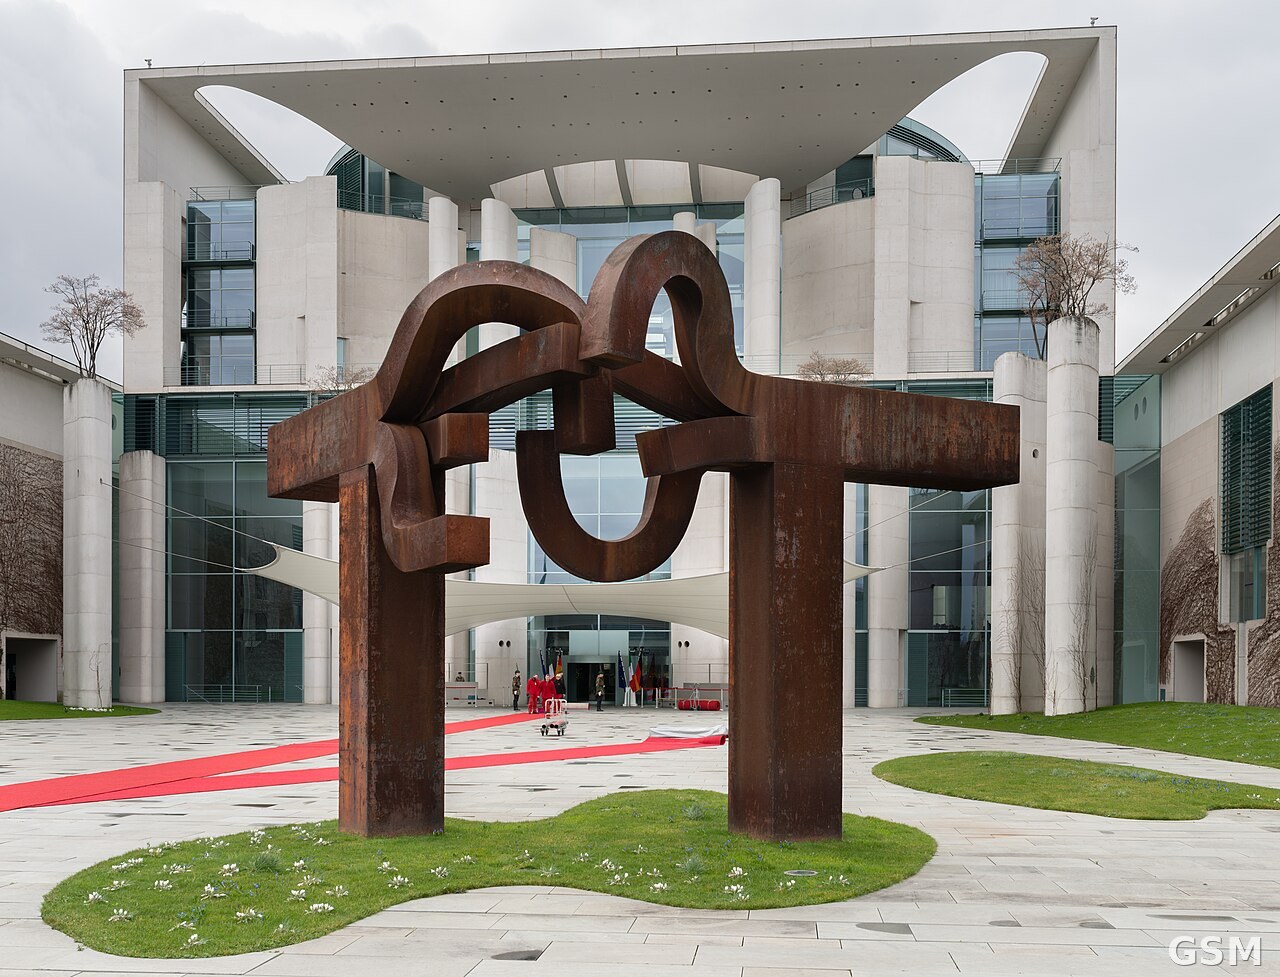
Photo: 柏林联邦总理府。图:Norbert Nagel,Wikimedia Commons,CC BY-SA 3.0。 / The Federal Chancellery in Berlin. Photo by Norbert Nagel, via Wikimedia Commons, CC BY-SA 3.0.