MUJI Operator's Second Report: Full Card Numbers of About 1.09 Million MUJI Card Members May Have Been Accessed, With Up to 27.26 Million Accounts Affected
Tokyo — Ryohin Keikaku, the Japanese retailer that operates MUJI, said in a second report on November 4 that the scope of an unauthorized external access incident involving its official app had widened: for about 1.09 million records of the MUJI Card co-branded credit card issued by Credit Saison, the full card numbers may have been accessed from outside, including about 345,000 cards that remain valid. The company's first report on October 30 had said credit card information was not affected; the second report reversed that statement.
The first report said that for up to about 27.26 million member records, including those of former members, email addresses, dates of birth, gender and member IDs may have been accessed. The second report confirmed that the scope was not limited to users of the official app but also included members of the MUJI online store, and that for about 520,000 of the records, names, addresses and telephone numbers were also involved.
The MUJI Card portion covers members who joined by July 2021: the full card number, the MUJI Card ID and the date of birth may have been accessed, while cardholder names, expiration dates and security codes were not included. Of the roughly 345,000 cards still valid, about 168,000 were in a state where they could be viewed together with information such as email addresses. For about 120 further records of cards registered through the app or the online store, the first six and last two digits of the card number and the cardholder name may have been accessed.
Why did the numbers remain in Ryohin Keikaku's systems years after the data link ended? According to the company, before July 2021 it obtained the card numbers and related data of MUJI Card members in order to verify membership and award points. That linkage ended in July 2021 and the current system no longer stores the data, but the old data was never deleted, remained in the system, and was not adequately protected. The company said this was a deficiency on its part.
Ryohin Keikaku said the unauthorized access had now been blocked, the official app and online store were operating as usual, and that as of the second report it had confirmed no leak of the information to the dark web and no damage from misuse. Credit Saison said it had found no unauthorized access to its own systems, had stepped up monitoring for fraudulent use, and that cardholders could contact it to have a card reissued. Ryohin Keikaku reminded customers that it never asks for credit card information by email or telephone and urged vigilance against suspicious contacts.
Source: Ryohin Keikaku
Published by GSM · USA (original Chinese edition)
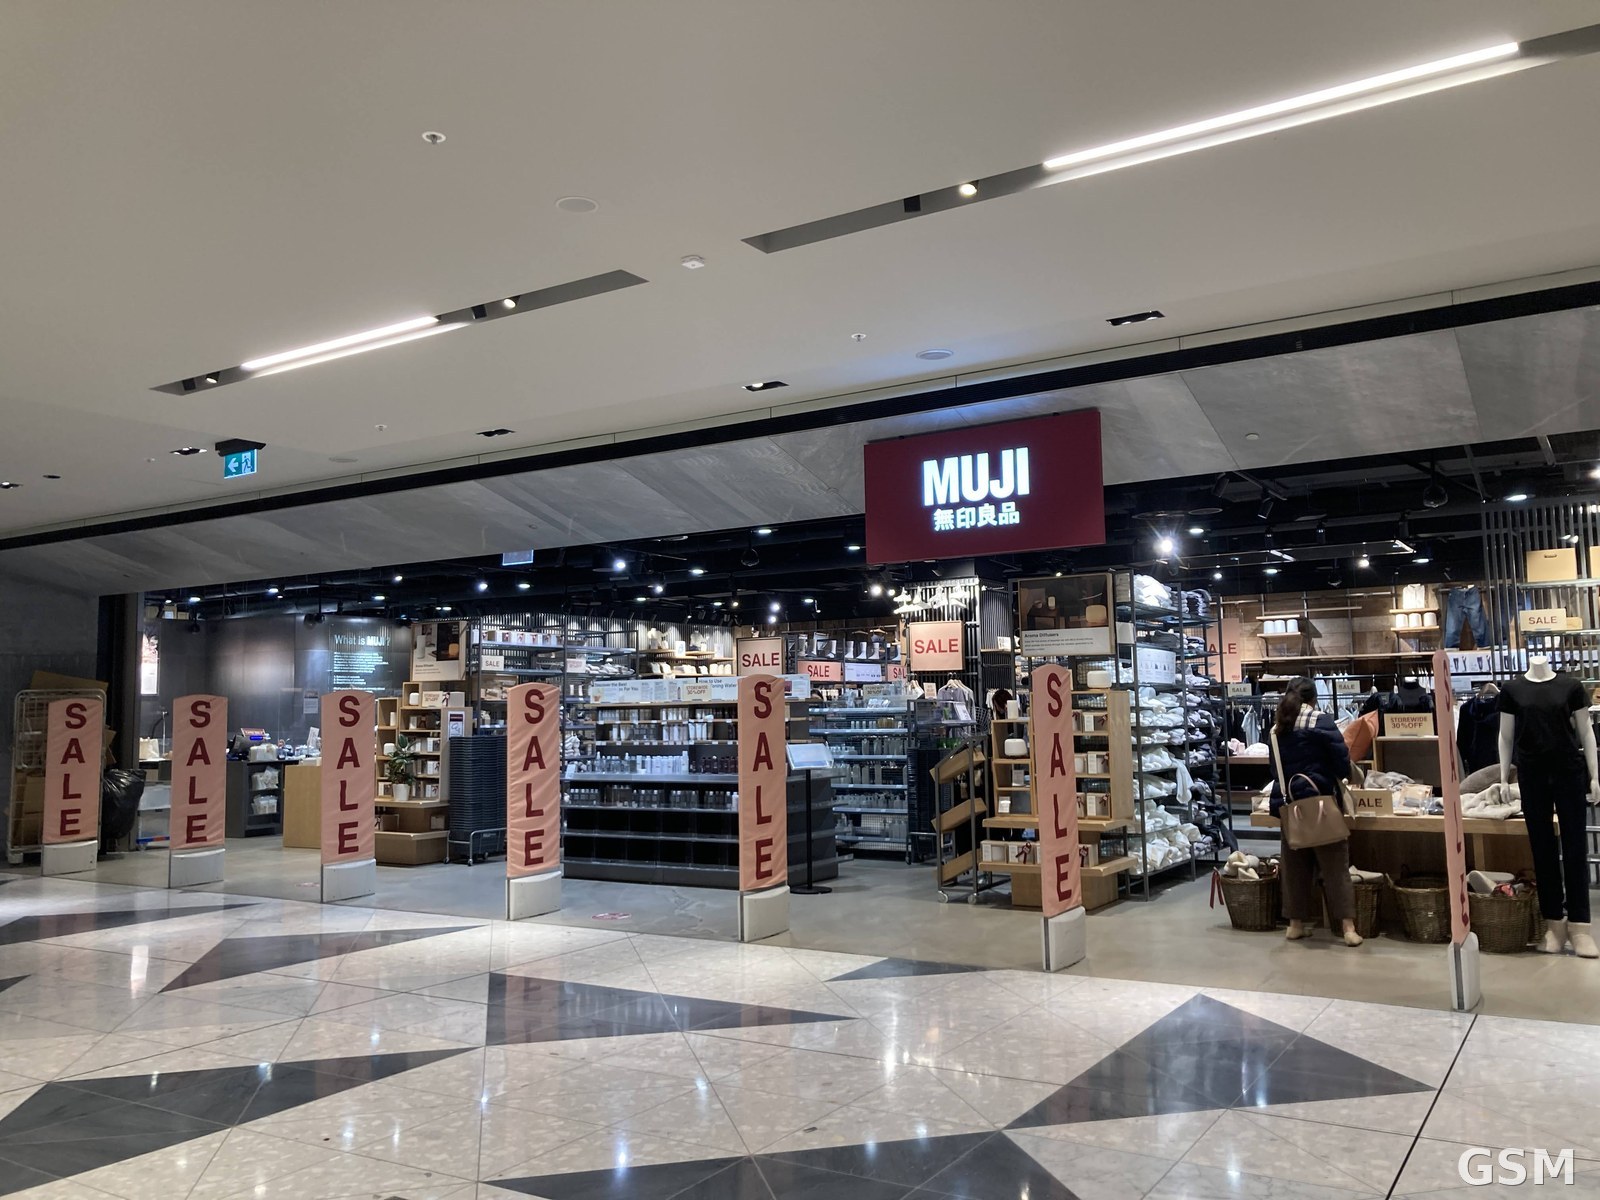
Photo: 图:一家无印良品(MUJI)门店。照片 CC BY-SA 4.0(Nick-D),经 Wikimedia Commons。 / Photo: A MUJI store. CC BY-SA 4.0 (Nick-D), via Wikimedia Commons.