Thai Airways Says About 60,529 Passenger Records Were Accessed Without Authorization; Card Data Unaffected
Thai Airways International said in a statement on November 9 that Amadeus IT Group, the provider of its passenger service systems, had informed it of a security incident involving unauthorized access to booking data stored in Amadeus systems between August 10, 2023, and September 23, 2026.
Based on the investigation to date, Thai Airways said, data from approximately 60,529 passenger records may have been accessed without authorization. The affected information included passenger names, booking references (PNRs), travel dates, flight routings and cabin classes. About 376 additional records may also have involved email addresses, telephone numbers, passport numbers, nationalities, frequent flyer numbers, flight numbers, ticket numbers and seat numbers. The airline stressed that passengers' credit card information was not affected, and that, as of the statement, it had not found that the data had been disclosed.
Amadeus has confirmed that the login credentials used in the unauthorized access have been revoked, all affected passwords have been reset, and monitoring and detection measures have been strengthened, Thai Airways said. The incident has not impacted the airline's own systems or operations.
Thai Airways said it has informed the relevant authorities and is continuing to investigate, including a thorough analysis of the data and information provided by Amadeus. Affected passengers will be notified individually once the relevant details have been verified, and the airline apologized for any concern or inconvenience caused.
Source: Thai Airways International
Published by GSM · USA (original Chinese edition)
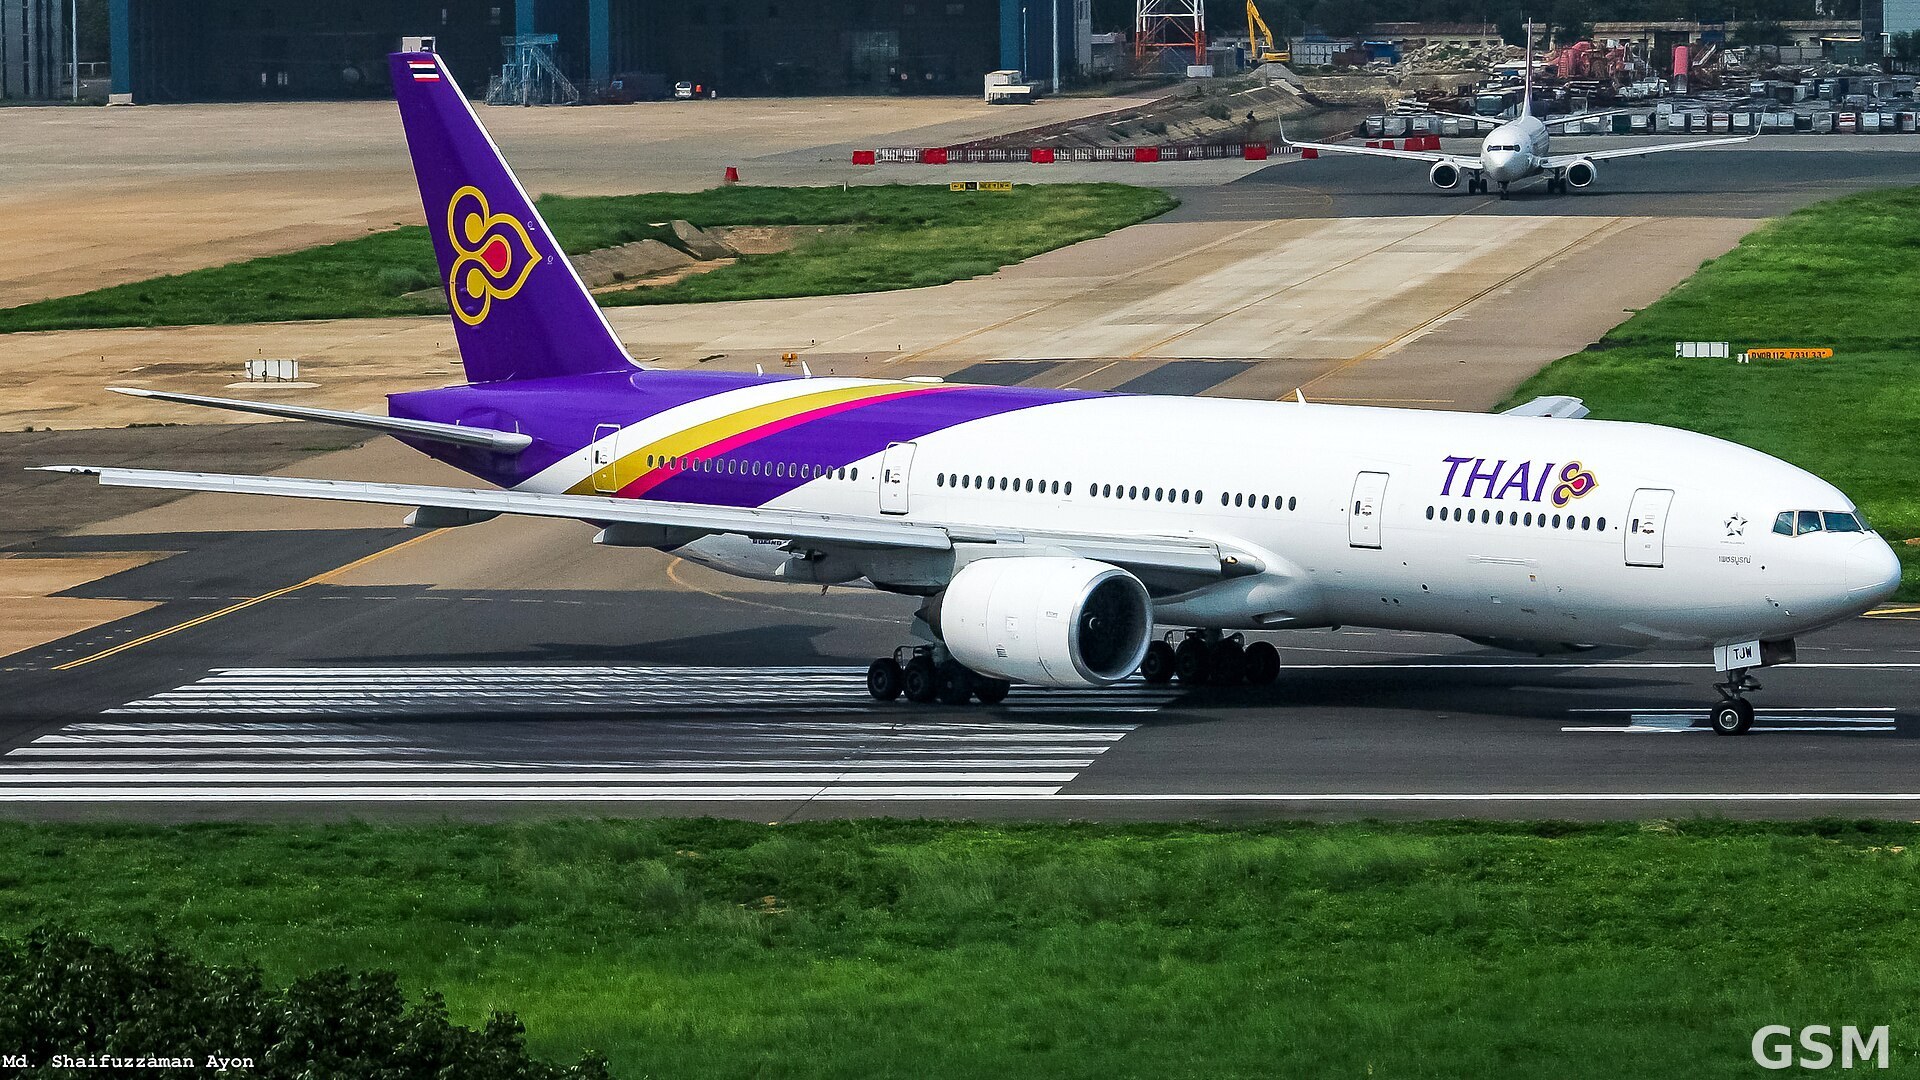
Photo: 图:泰国国际航空一架波音 777-200ER 客机(资料图)。Wikimedia Commons,CC BY-SA 4.0。 / Photo: A Thai Airways Boeing 777-200ER (file photo). CC BY-SA 4.0, via Wikimedia Commons.