DOJ-led international operation disrupts Gootloader malware: more than 100 servers cleaned, at least 25,000 computers infected
The U.S. Department of Justice (DOJ) announced on November 12 that, in an international law enforcement operation, officers had removed malware known as Gootloader from more than 100 computer servers, including compromised WordPress sites, and seized U.S. domain names used by criminals to deliver and control the malware.
Since 2018, Gootloader has infected at least 25,000 computers around the world and has been used in ransomware attacks on at least 44 U.S.-based victims, resulting in approximately $28.8 million in losses, the department said. Its targets included the U.S. Department of War and the Defense Industrial Base.
Assistant Attorney General A. Tysen Duva of the Justice Department's Criminal Division said that, with court authorization, the department and the FBI, along with international partners, conducted an online operation that liberated more than 100 servers from malicious software, denying ransomware criminals a platform. U.S. Attorney Peter McNeilly for the District of Colorado said cybercrime knows no borders and called the case an example of international partnerships protecting people around the world.
According to warrants unsealed this week, Gootloader infects computers by tricking users into downloading it. Infected computers are added to a botnet of other compromised machines, which the operators use to infect still more computers and then sell access to those machines to ransomware actors.
The actions were conducted in coordination with Operation Endgame, a multinational initiative targeting malware services used by cybercriminals. The investigation was led by the Defense Criminal Investigative Service (DCIS), the FBI's Denver Field Office and the Army Criminal Investigation Division, working with law enforcement in Germany, the Netherlands, Canada, Denmark, France, the United Kingdom and Australia, and with Europol. The Shadowserver Foundation assisted internet service providers and computer security incident response teams in identifying infected systems, notifying victims and helping with remediation.
Senior Counsel Thomas Dougherty of the Criminal Division's Computer Crime and Intellectual Property Section and Assistant U.S. Attorney Jasand Mock for the District of Colorado are prosecuting the case, with assistance from the Justice Department's Office of International Affairs. (Source: U.S. Department of Justice)
Source: U.S. Department of Justice
Published by GSM · USA (original Chinese edition)
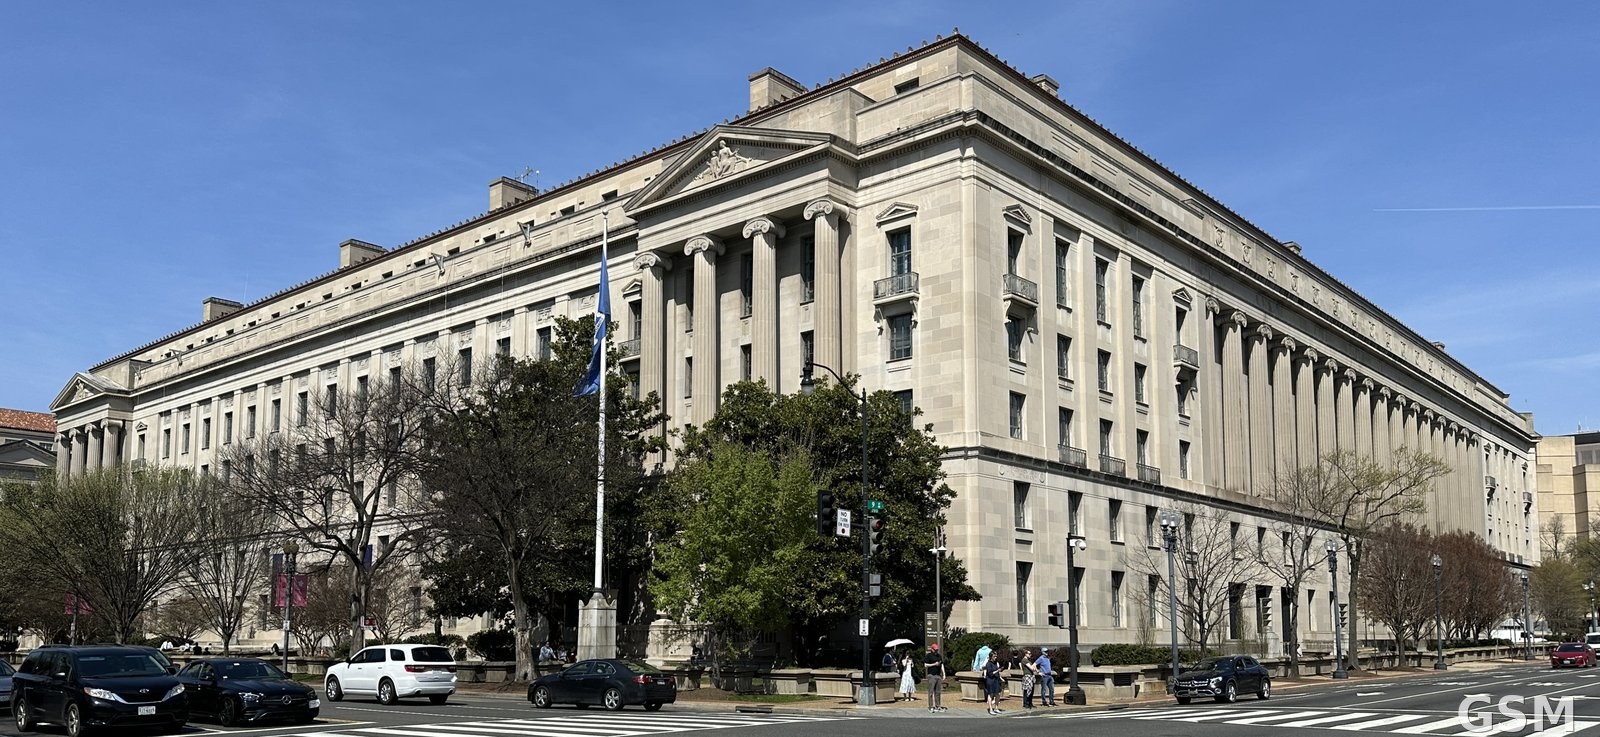
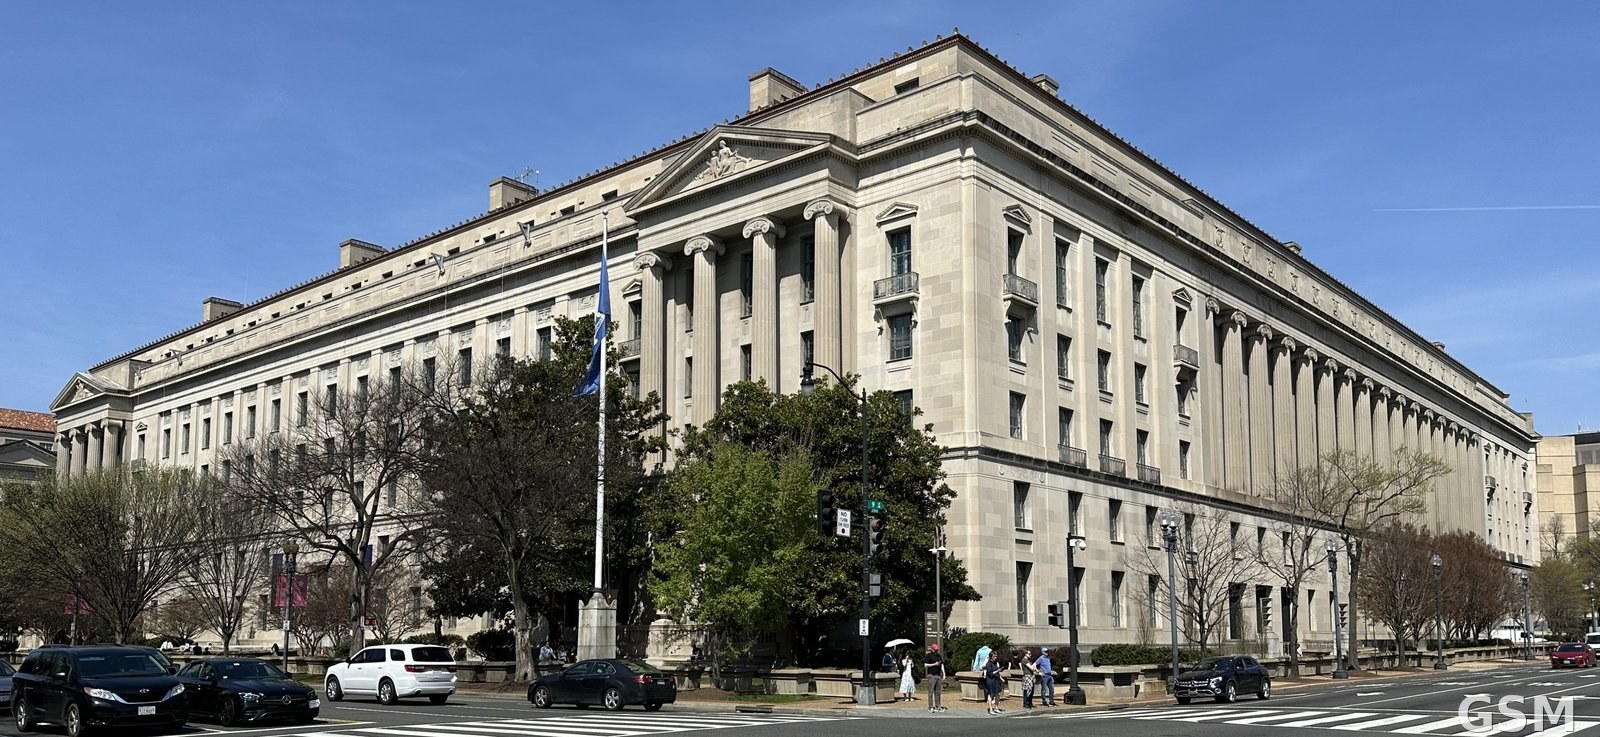
Photo: 图:美国司法部总部大楼(华盛顿,资料图)。四级图库联邦核心包,司法部大楼固定图。 / Photo: U.S. Department of Justice headquarters building in Washington (file photo). Federal core asset pack.