
Follow-Up: Ryohin Keikaku President Satoshi Shimizu Apologizes Over MUJI Data Breach, Admitting About 1.09 Million Card Numbers Were Kept Unencrypted and Should Have Been Deleted
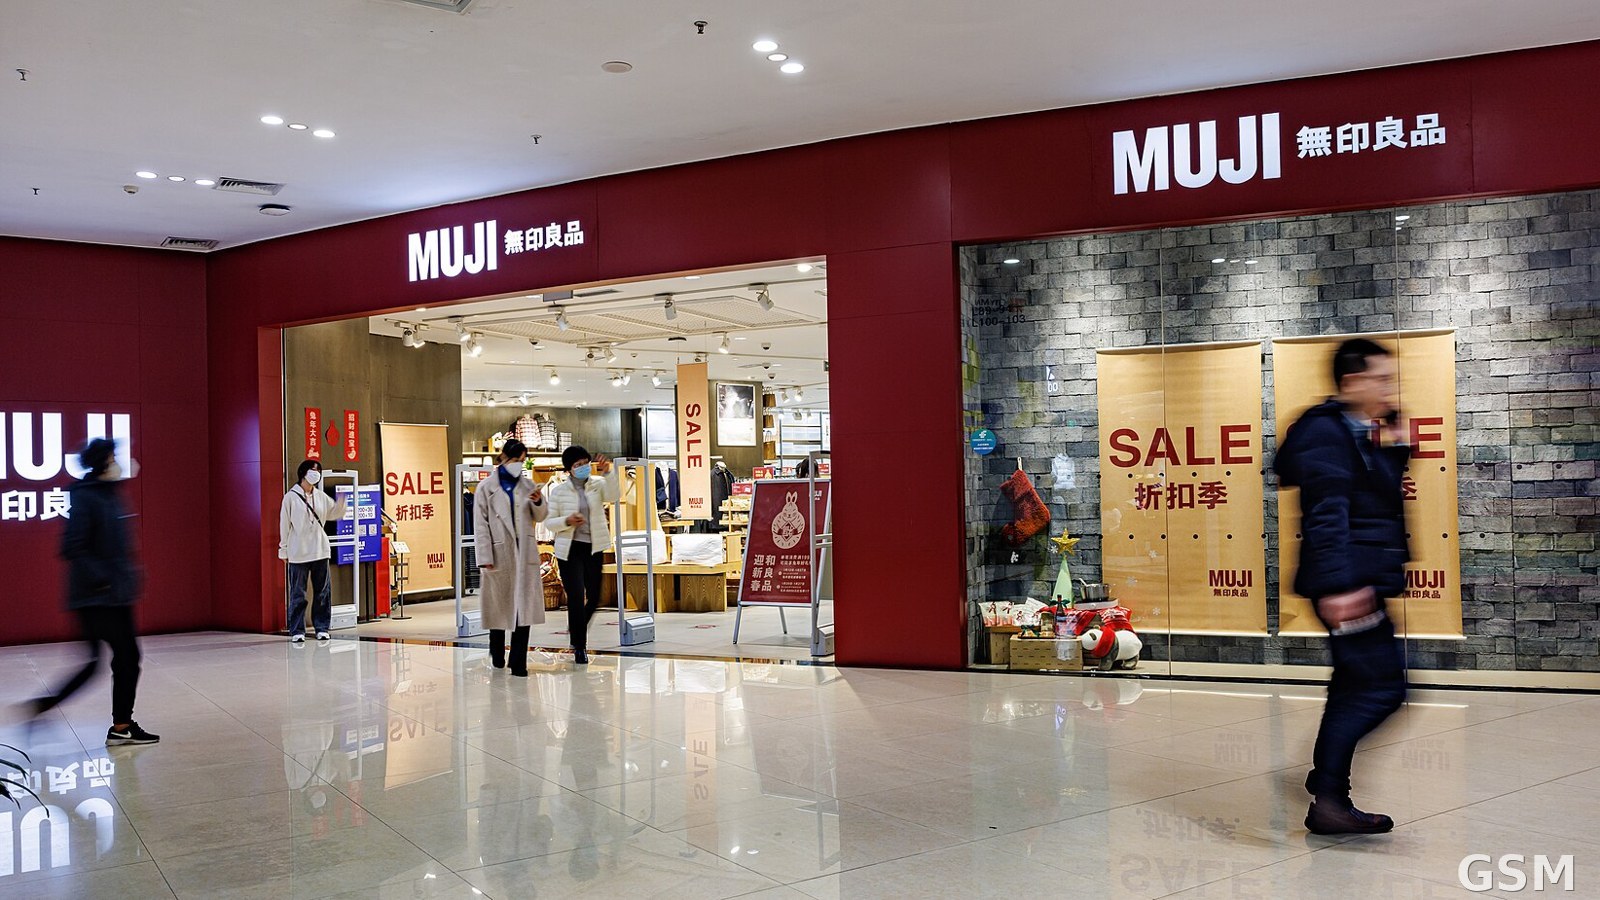
Satoshi Shimizu, president of Ryohin Keikaku, the Japanese company that operates MUJI, apologized at a Tokyo press conference on November 12 over the unauthorized access to the brand's app and online store that may have exposed customer information. He admitted that the full card numbers of about 1.09 million MUJI Card credit cards were retained after they should have been deleted, and were stored without masking or encryption, calling it a failure in the company's data management.
Ryohin Keikaku has issued four updates on the incident. Its first report, on October 30, said the official app had been accessed without authorization and that up to about 27.26 million customer records could be affected; the second report, on November 4, confirmed that the full numbers of about 1.09 million MUJI Card accounts might have been accessed externally. Shimizu explained that until July 2021 the company used card numbers to identify MUJI Card members and grant them benefits; after the rewards system changed that month, the numbers should have stopped being collected and been deleted, but they were not. The cards were issued by Credit Saison, and about 345,000 of them are still valid.
The fourth report, on November 9, added new findings: a credential-stuffing attack detected on November 7 may have exposed about 270,000 purchase-history records, and roughly 440,000 cash-on-delivery recipient records from January 2020 to February 2025 were newly included in the possible scope, raising records containing names and addresses from about 520,000 to about 750,000. MUJI's online store has been suspended since November 6, with no date set for reopening; all users will be required to reset their passwords when it reopens.
The company said it will bear the cost of reissuing affected MUJI Cards and began notifying affected customers by email and post on November 10. MUJI China said on November 6 that Chinese consumer information had been checked and confirmed safe, and was unrelated to the incident in Japan.
(Source: Kyodo News)
Source: Kyodo News
Published by GSM · USA (original Chinese edition)
Photo: 图:一家无印良品门店(CC BY-SA 4.0,经 Wikimedia Commons)。 / Photo: A MUJI store (CC BY-SA 4.0, via Wikimedia Commons).
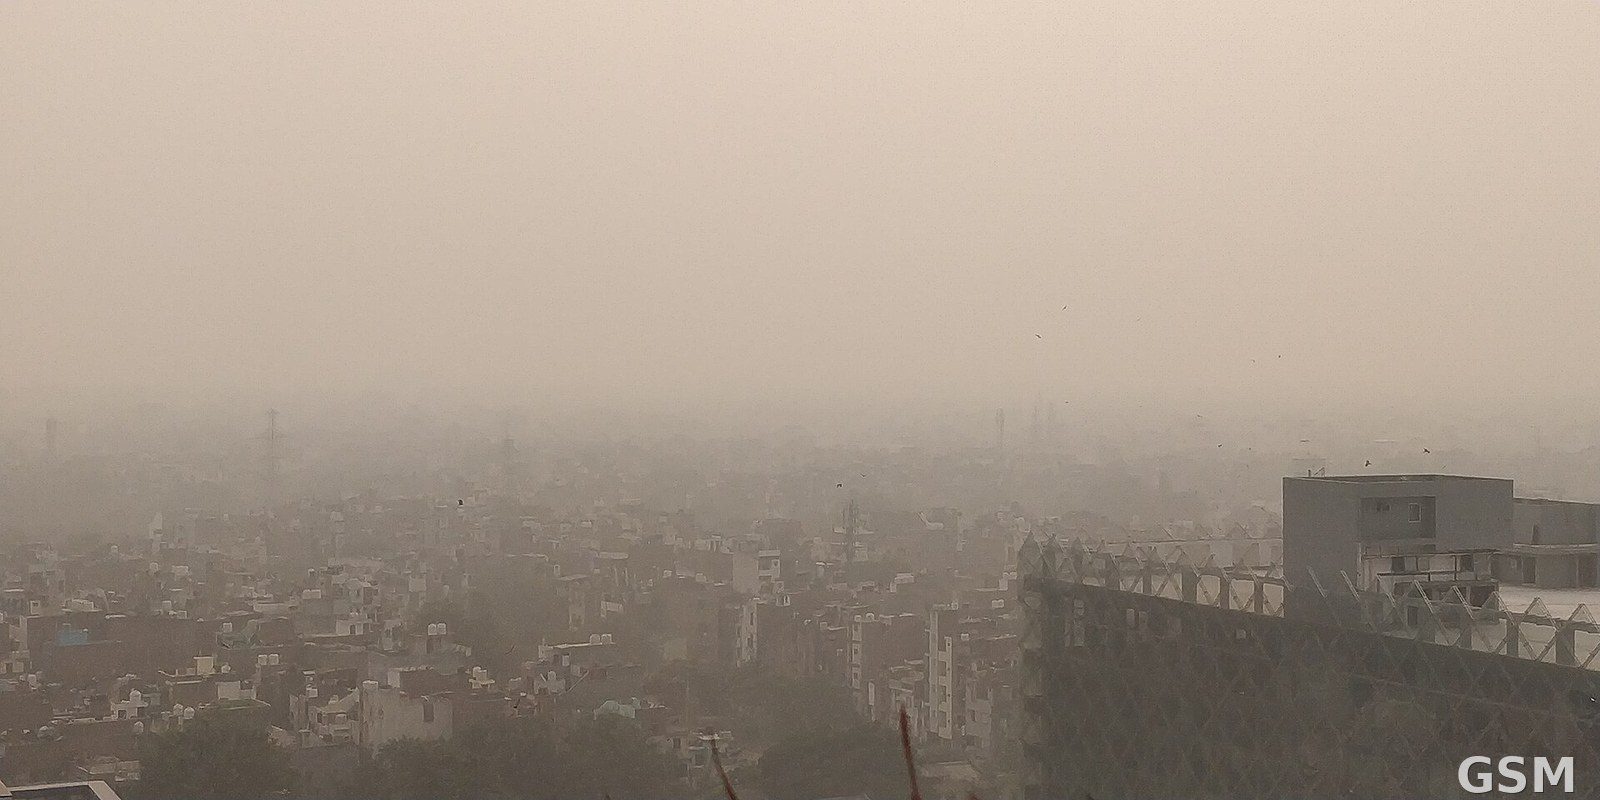 Delhi Overtakes Lahore on November 13 as the World's Most Polluted Major City: IQAir Reads the Air Quality Index at a Hazardous 334, While India's Central Pollution Control Board Reads 403 and Rates It Severe2026-11-13
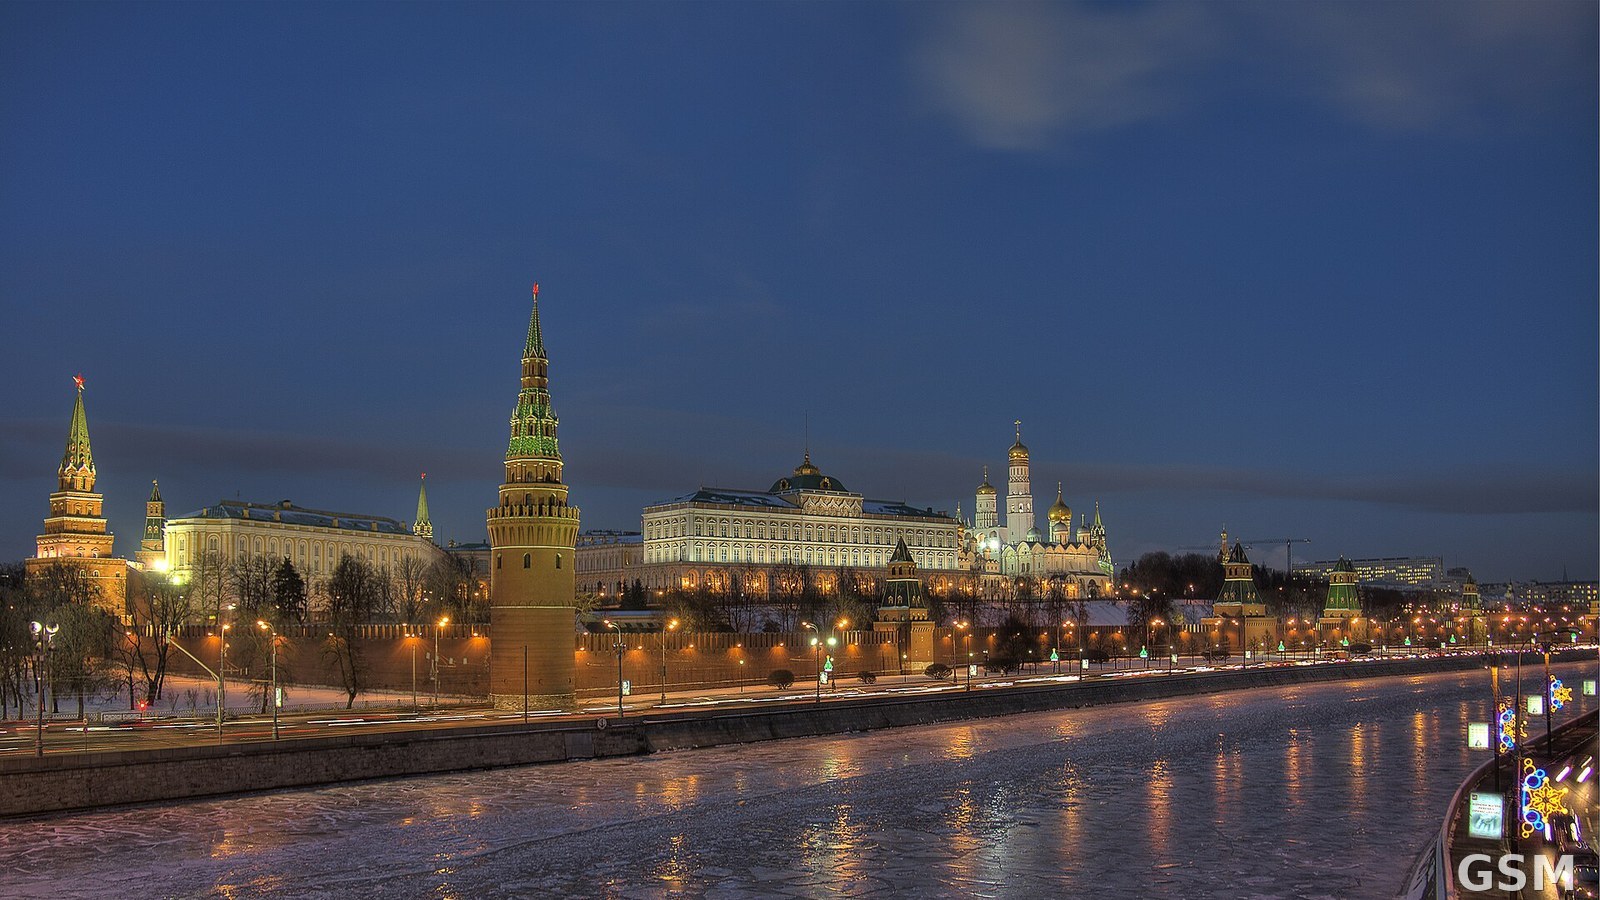 A Second Car Bomb in Two Days in Russia Explodes in Moscow on November 13: Russian Media Say the Car Belonged to Exiled Ukrainian Political Aide Sergei Zavorotniy, Who Was Hospitalised, and the Investigative Committee Has Opened an Investigation2026-11-13