Johnson Controls and Two Subsidiaries to Pay $5 Million to Settle Federal Cybersecurity Fraud Allegations
The U.S. Attorney's Office for the Northern District of Georgia announced on November 13 that Johnson Controls, Inc., a Milwaukee-based heating, ventilation, and air conditioning supplier, and two subsidiaries have agreed to pay $5 million to resolve allegations that they violated the False Claims Act by failing to comply with cybersecurity requirements in their federal contracts and subcontracts for building products and services. The two subsidiaries are Johnson Controls Fire Protection LP and Johnson Controls Security Solutions LLC.
According to the Justice Department, from January 2018 to August 2025, Johnson Controls and the two subsidiaries entered into contracts and subcontracts with NASA and the Departments of Defense, Energy, and Justice that required the companies to implement security controls to protect government information.
The government alleged that Johnson Controls failed to control access to protected information due to insufficient knowledge of, and insufficient control over, its information systems. It also allegedly failed to maintain a System Security Plan that met requirements for certain government contracts, and failed to adequately document, fully develop, or fully implement a plan of action and milestones to correct deficiencies and reduce or eliminate vulnerabilities in its information systems.
The settlement resolves two qui tam whistleblower lawsuits filed under the False Claims Act by former Johnson Controls employees Kelly Vance and David Thomas. The settlement provides for Vance to receive an $850,000 share. The cases are United States ex rel. Kelly Vance v. Johnson Controls, Inc. in the Northern District of Georgia and United States ex rel. David Thomas v. Johnson Controls Int'l PLC in the District of Columbia.
"Cybersecurity requirements are of the utmost importance to the government," said U.S. Attorney Theodore S. Hertzberg. "My office will vigorously pursue contractors who fail to follow these requirements, particularly when those failures persist over several years, needlessly exposing our nation to malevolent attacks and exploitation by bad actors." Assistant Attorney General Jonathan Guynn of the Justice Department's Civil Division said federal contractors must follow required cybersecurity standards to safeguard sensitive government information.
The resolution was the result of a coordinated effort between the U.S. Attorney's Offices for the Northern District of Georgia and the District of Columbia; the Justice Department Civil Division, Commercial Litigation Branch; Defense Criminal Investigative Service; NCIS; Air Force Office of Special Investigations; NASA OIG; Department of Energy OIG; the Department of Justice OIG; and GSA OIG. The matter was handled by Assistant U.S. Attorney Adam Nugent, Trial Attorney Jennifer Cook, and Assistant U.S. Attorney Sean Tepe for the District of Columbia.
(Source: U.S. Department of Justice)
Source: U.S. Department of Justice
Published by GSM · USA (original Chinese edition)
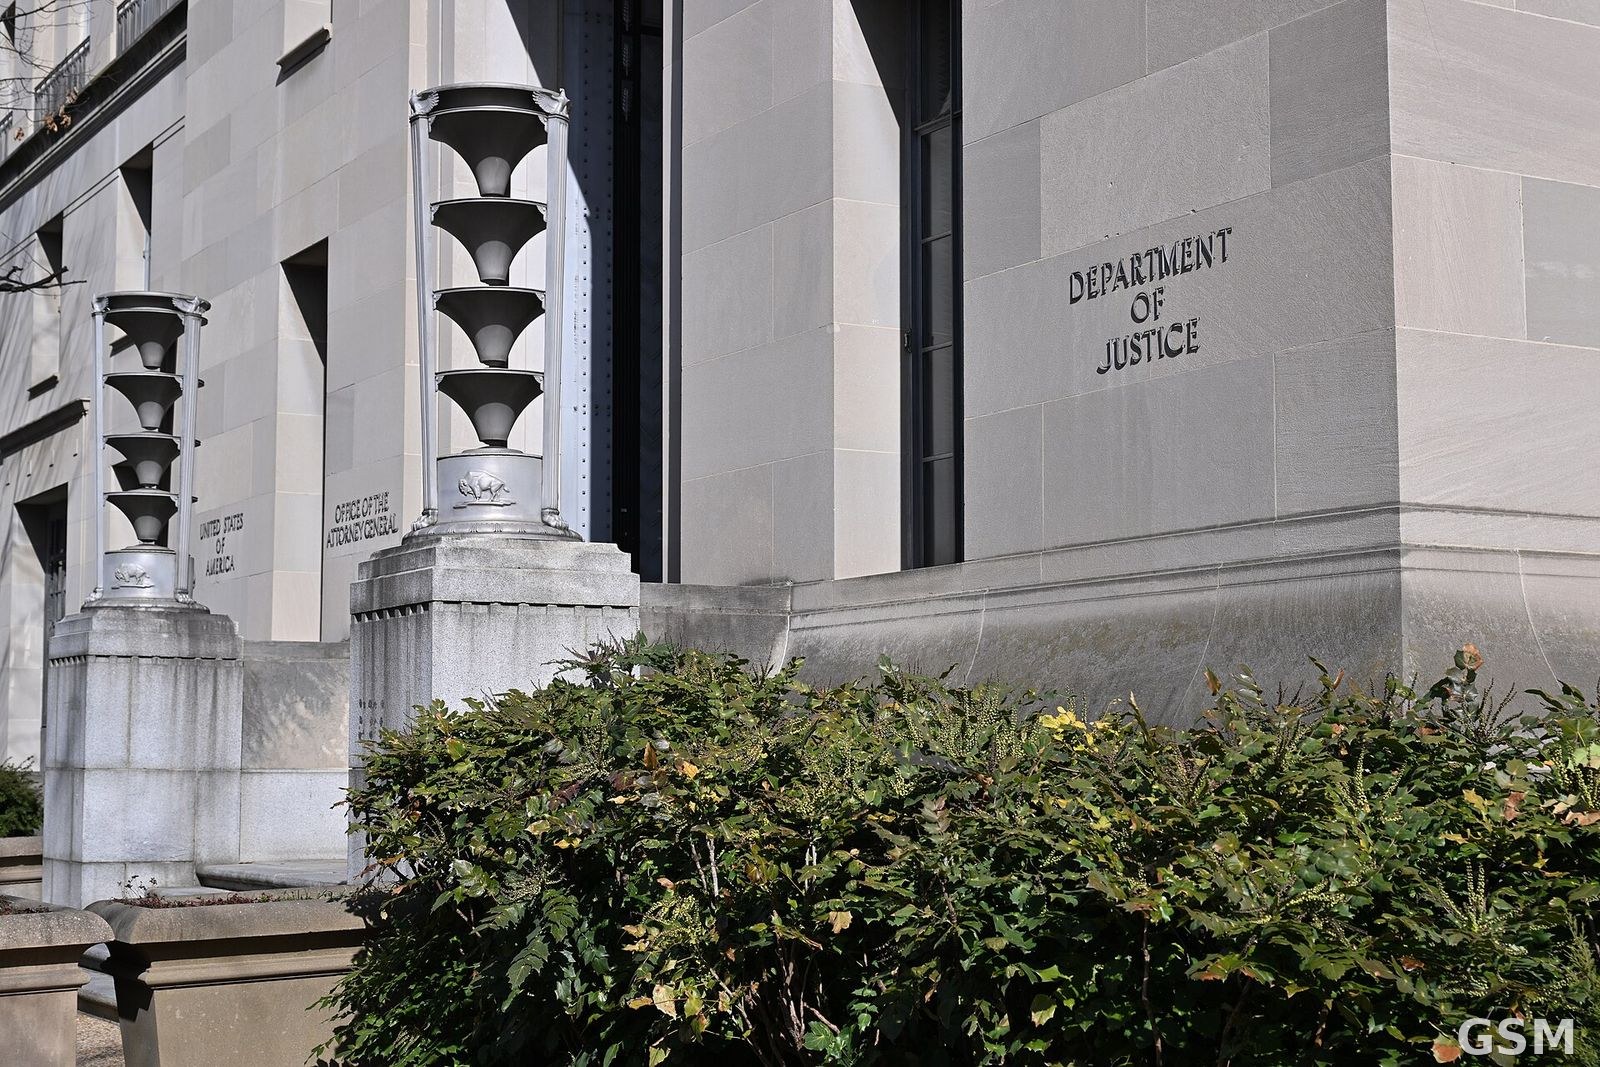
Photo: 图:美国司法部本部大楼入口石墙特写,刻有 DEPARTMENT OF JUSTICE 字样(固定图库联邦核心包)。G. Edward Johnson 摄,CC BY 4.0,经 Wikimedia Commons。 / Photo: Entrance wall of the U.S. Department of Justice headquarters engraved with DEPARTMENT OF JUSTICE (fixed federal-core asset-pack image). Photo by G. Edward Johnson, CC BY 4.0, via Wikimedia Commons.