HHS Settles Ransomware Investigation of Lehigh Valley Health Network for $800,000 After Breach Affecting 248,359 People
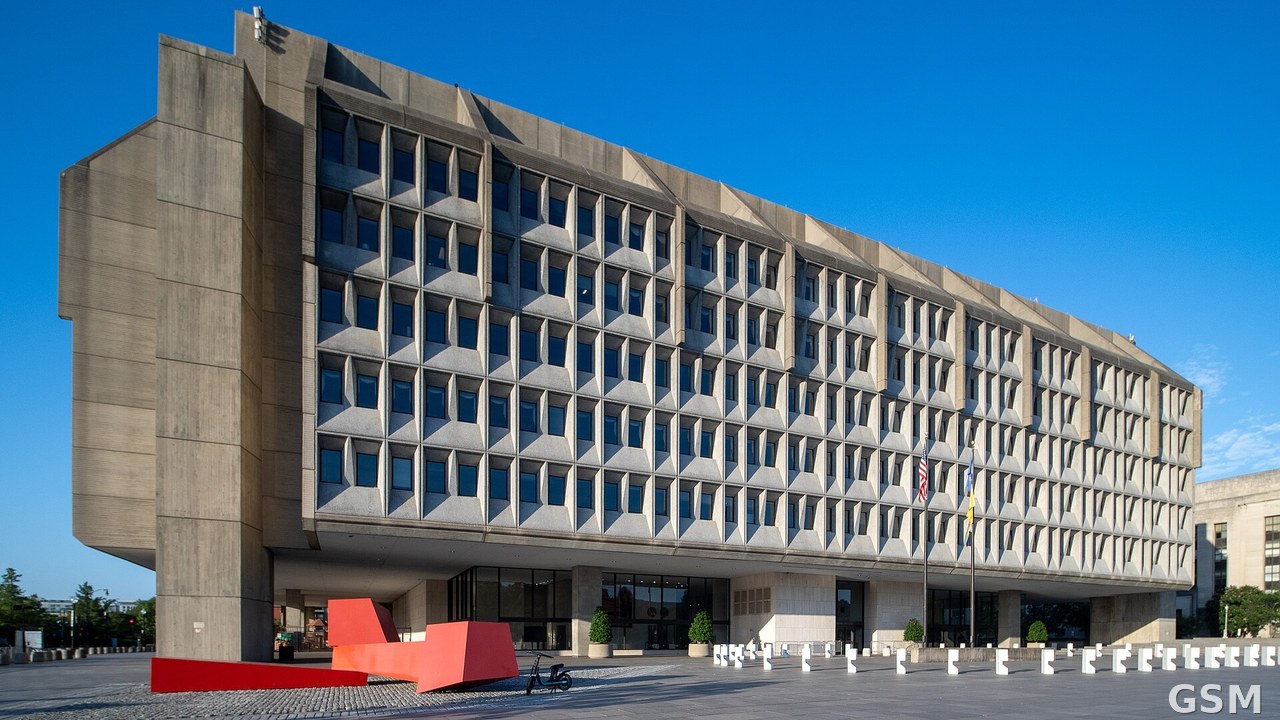
The Office for Civil Rights (OCR) of the U.S. Department of Health and Human Services (HHS) announced in Washington on October 29 that it has reached a settlement with Lehigh Valley Health Network (LVHN), a health system in Pennsylvania, and its affiliated covered entities, resolving an investigation into potential violations of the HIPAA Privacy, Security, and Breach Notification Rules. LVHN agreed to pay $800,000 and to implement a corrective action plan that OCR will monitor for three years.
The settlement marks OCR's 22nd ransomware enforcement action. According to HHS, LVHN filed a breach report on May 15, 2023, stating that on February 4, 2023, it discovered suspicious activity in its IT system that was later determined to be ransomware. Protected health information (PHI) was exfiltrated and posted on the dark web, affecting 248,359 individuals.
The information involved included sensitive photographs of cancer patients receiving radiation oncology treatment, as well as names, addresses, dates of birth, Social Security numbers, driver's license numbers, financial information, diagnoses and conditions, lab results, medications, and treatment information.
OCR found that LVHN had potentially violated the rules by failing to conduct an accurate and thorough risk analysis of the risks and vulnerabilities to all of its electronic PHI; failing to implement procedures to regularly review records of information system activity such as audit logs, access reports, and security incident tracking reports; impermissibly disclosing the PHI of 248,359 individuals; failing to timely notify affected individuals; and failing to timely notify the Secretary of HHS.
Under the corrective action plan, LVHN committed to conduct an accurate and thorough risk analysis, develop and implement a risk management plan, review and revise its Privacy, Security, and Breach Notification Rule policies and procedures as needed, and review and revise its HIPAA training materials for workforce members.
"Failure to conduct an accurate and thorough risk analysis and to undertake regular review of information system activity makes regulated entities attractive targets for cyberattacks," said OCR Director Paula M. Stannard. "The best defense against cyberattacks is full implementation of the HIPAA Security Rule."
HHS also recommended that regulated entities identify where electronic PHI is located and how it flows through their systems, periodically conduct and update risk analyses, ensure audit controls are in place, regularly review information system activity, authenticate users, encrypt electronic PHI in transit and at rest, incorporate lessons learned from incidents into their security management processes, and provide workforce members with regular HIPAA training specific to their job duties.
Source: GSM · USA (original Chinese edition)
Photo: 图:位于华盛顿的美国卫生与公众服务部总部 Hubert H. Humphrey 大楼外景。ajay_suresh 摄,经 Wikimedia Commons,授权 CC BY 2.0。 / Photo: The Hubert H. Humphrey Building, headquarters of the U.S. Department of Health and Human Services in Washington. Photo by ajay_suresh, via Wikimedia Commons, CC BY 2.0.