Adaptive Hybrid Intrusion Detection Framework AHIDF Reaches 0.89 Accuracy and AUC up to 0.92
A study published November 14 in Scientific Reports proposes the Adaptive Hybrid Intrusion Detection Framework, AHIDF, which combines signature-based, machine learning-based and deep learning-based detectors in a single framework, in response to increasingly sophisticated cyberattacks that strain single-detector, static rule-based systems.
At its core is a new Adaptive Confidence-Weighted Decision Fusion mechanism, ACWDF, which dynamically weights each detector's output based on the detector's effectiveness in recent operations. The study also proposes an Operational Intrusion Detection Readiness Score, OIDRS, to assess detection capability, discriminative performance, false alarm behavior, latency and computational overhead together.
Experimental results showed accuracy of 0.89, precision of 0.88, recall of 0.86 and an F1 score of 0.87 across the categories of cyberattacks, with ROC analysis reaching an AUC of up to 0.92.
The authors are affiliated with A.V.C. College of Engineering, Vel Tech Rangarajan Dr. Sagunthala R&D Institute of Science and Technology and Panimalar Engineering College in India.
The authors say the adaptive decision fusion enhances detection robustness and operational readiness, and that the framework offers a realistic, scalable approach for today's cybersecurity environment. The research received no specific grant from any funding agency.
Source: Scientific
Published by GSM · USA (original Chinese edition)
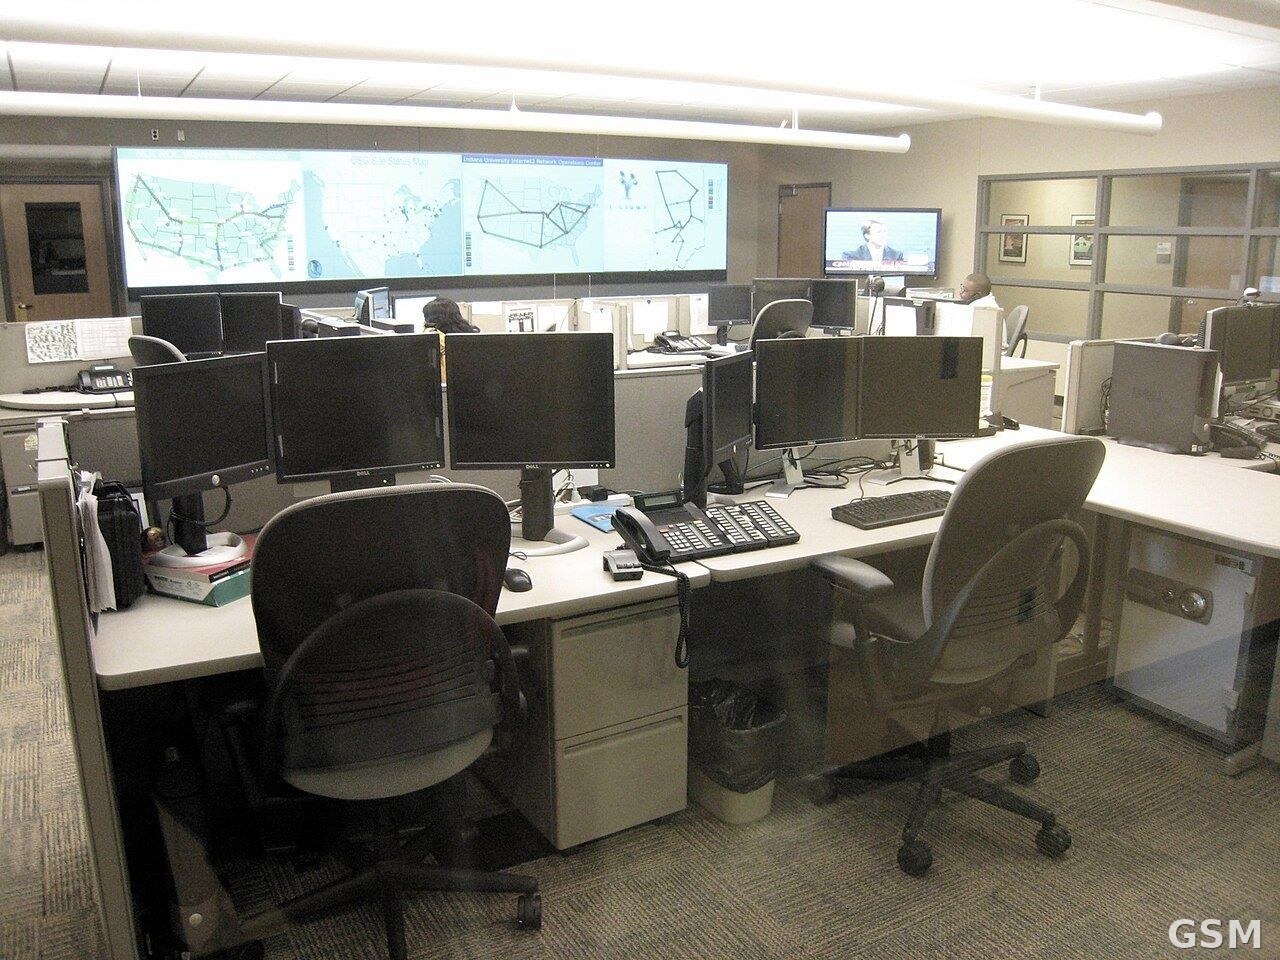
Photo: 图:Indiana University 的网络运营中心,墙面大屏显示网络状态地图。来源:Alan Levine,Wikimedia Commons,CC BY 2.0。 / Photo: The network operations center at Indiana University, with network status maps on the wall displays. Source: Alan Levine, Wikimedia Commons, CC BY 2.0.